-
KOR
-
CONTACT
-
DOWNLOAD
- Main Product
- Power Transformer
- Gas Insulated Switchgear
- High-voltage Motor
- Generator
- MV/LV Switchgear
- Distribution Transformer
- Low-voltage Motor
- MV/LV Circuit Breaker
Search in other ways


Power Generation
Transmission
Distribution
Consumer/Factory


- 1~9, A~D
- 145kV GISHigh-voltage Switchgear
- 170kV GISHigh-voltage Switchgear
- 245/300kV GISHigh-voltage Switchgear
- 362kV GISHigh-voltage Switchgear
- 420/550kV GISHigh-voltage Switchgear
- 72.5kV GISHigh-voltage Switchgear
- 800kV GISHigh-voltage Switchgear
- Asset Management SolutionINTEGRICT
- BUSDUCT(BUSDUCT)Switchgear
- BUSDUCT(BUSWAY)Switchgear
- Cast Resin Distribution TransformerDistribution Transformer
- C-GISSwitchgear
- Crown Triton Motor Large FrameLow-voltage Motor
- DPRS, TPRS TransformerSpecial Transformers
- Drip-proof MotorLow-voltage Motor
- Dry-air switchgearGREENTRIC
- E~L
- Eco Shaft GeneratorGREENTRIC
- Emergency Switchboard Marine Switchgear
- Energy SolutionINTEGRICT
- Ex d/de/db/dbeb IIB/C MotorLow-voltage Motor
- Ex eb/ec IIC MotorLow-voltage Motor
- Furnace TransformerSpecial Transformers
- Gas Insulated TransformerSpecial Transformers
- General/Explotion Proof MotorHigh-voltage Motor
- Group Starter PanelMarine Switchgear
- High-Efficiency/Low Noise TransformerSpecial Transformers
- High Speed MotorElectric Motor
- HVDC Converter TransformerSpecial Transformers
- IE4 LV MOTORGREENTRIC
- IEEE841 MotorLow-voltage Motor
- L/M Voltage Circuit...L/M Voltage Circuit Breaker
- Low Voltage SwitchgearSwitchgear
- LV SwitchboardMarine Switchgear
- M~R
- Marine Distribution...Marine Distribution Transformer
- Marine Rotating MachineMarine Rotator
- Marine TransformerSpecial Transformers
- Medium/Low SpeedGenerator
- Mobile TransformerSpecial Transformers
- Motor Control Panel(MCP)Marine rotator
- MV SWGR for NuclearSwitchgear
- MV SwitchboardMarine Switchgear
- MV SwitchgearSwitchgear
- Natural Ester/Synthetic Oil-immersed Power TransformerSpecial Transformers
- Natural Ester/Synthetic Oil-immersed Power TransformerGREENTRIC
- Oil-immersed Distribution TransformerDistribution Transformer
- Phase Shift TransformerSpecial Transformers
- Power TransformerPower Transformer
- Quarry & Crusher Duty MotorLow-voltage Motor
- RMUSwitchgear
- S~Z
- SF6-Free GISGREENTRIC
- Shunt ReactorPower Transformer
- SVC TransformerSpecial Transformers
- Synchronous MotorHigh-voltage Motor
- TEAAC Type Squirrel-cage MotorHigh-voltage Motor
- TEFC MotorLow-voltage Motor(KS/IEC)
- TEFC MotorLow-voltage Motor(NEMA)
- TEFC Type Squirrel-cage MotorHigh-voltage Motor
- TEWAC Type squirrel-cage MotorHigh-voltage Motor
- Thruster StarterMarine Switchgear
- Totally-enclosed Wound-rotor MotorHigh-voltage Motor
- Trackside TransformerSpecial Transformers
- UL Explosion ProofLow-voltage Motor
- Weather Protected TEFC MotorHigh-voltage Motor
- Weather Protected Wound-rotor MotorHigh-voltage Motor
- Weather Protected WPIIHigh-voltage Motor
HD Hyundai Electric
Cybersecurity Center
HD Hyundai Electric has established a cybersecurity framework based on international security standards
to ensure the safe operation of its products and services. We have obtained global certifications including
ISO/IEC 27001, and manage security risks primarily through the CISO (Chief Information Security Officer)
organization.
- Cybersecurity Center
- Security Activity Notifier
- Security Notice
- Report Vulnerabilities
Introduction to Security Activity Notifier
HD Hyundai Electric systematically manages cybersecurity across all products and services based on international standards and global security frameworks.
-

Based on international standards
-

Conducting regular audits
-

Continuous Improvement
-

Transparent disclosure
Cybersecurity Management System
HD Hyundai Electric has established an Information Security Management System (ISMS) based on ISO/IEC 27001 and operates enterprise-wide cybersecurity governance,
including product security and service security.
-
Governance
- Operate a security organization led by the CISO
- Manage enterprise security policies and guidelines
-
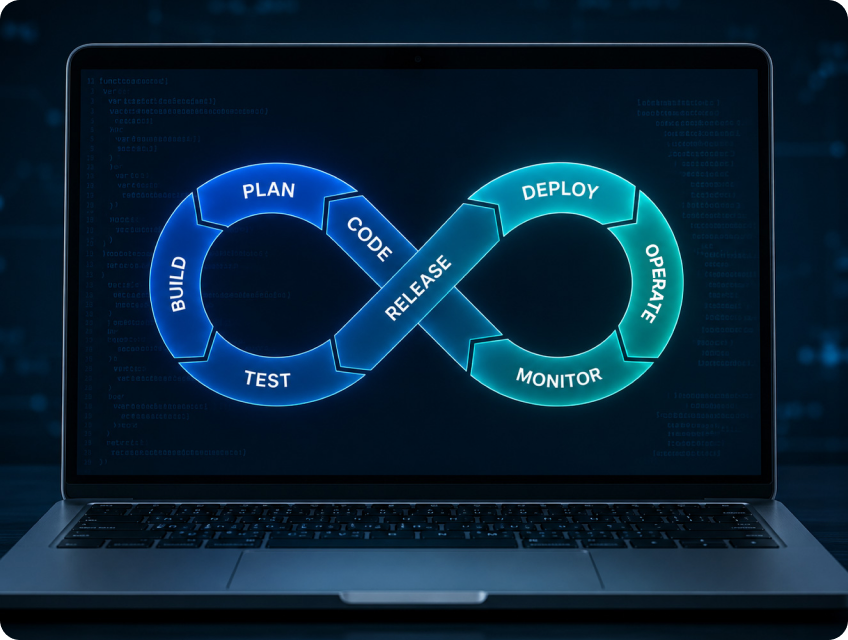
Secure SDLC
- Incorporate security requirements from the design stage
- Conduct static/dynamic analysis and security testing
-
Operations security
- Security Monitoring
- Manage vulnerabilities and operate the patch process
Certification and Standard Compliance Status
| Sortation | Certification/Standardization | Scope of application | Initial certification | Recent update | Link |
|---|---|---|---|---|---|
| Regulatory & Standards | IEC62443-4-1 | Enterprise Secure SDLC | 2026 | 2026 | View |
| Enterprise Security | SOC2 TYPE Ⅱ | Ulsan Transformer Factory, Alabama Factory | 2026 | 2026 | View |
| Product Security | UR E27 | Motor Predictive Diagnostic System(HiPDS) | 2026 | 2026 | |
| Enterprise Security | ISO/IEC 27001:2022 | Enterprise | 2021 | 2024 |
Audit and Evaluation Activities
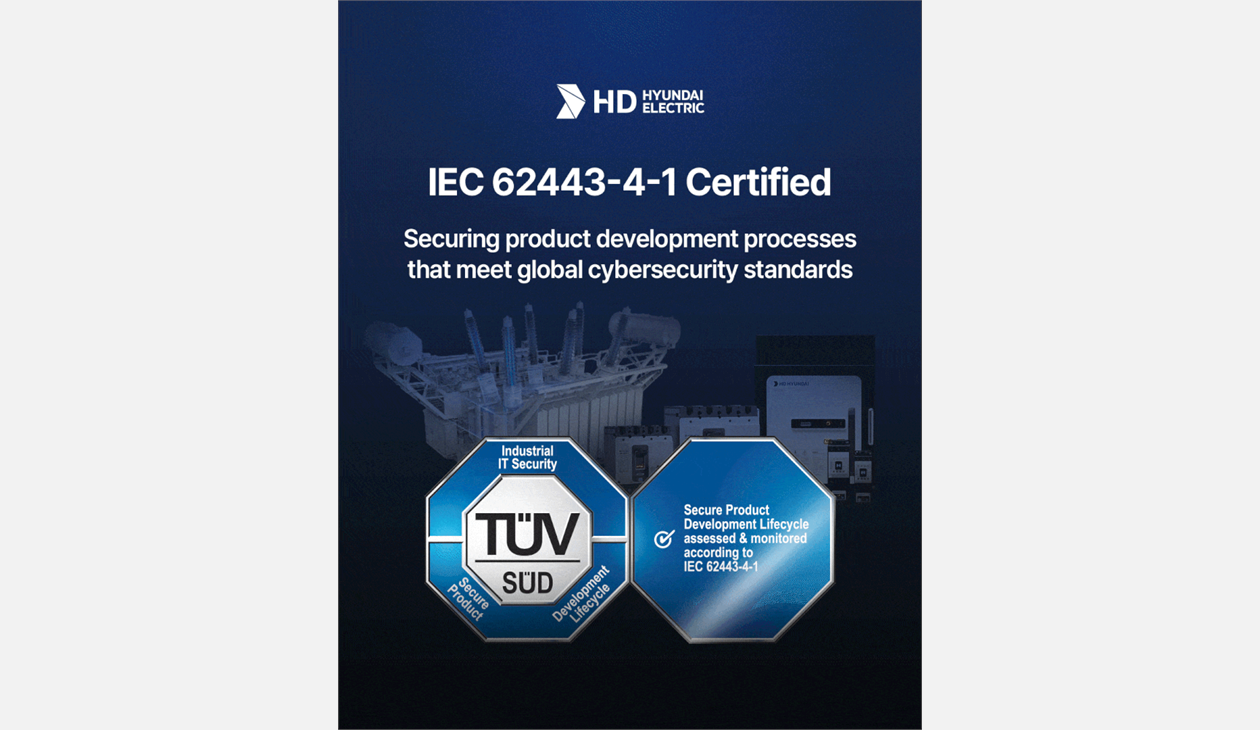
2026.06IEC 62443-4-1 (ML2) Certification Achieved
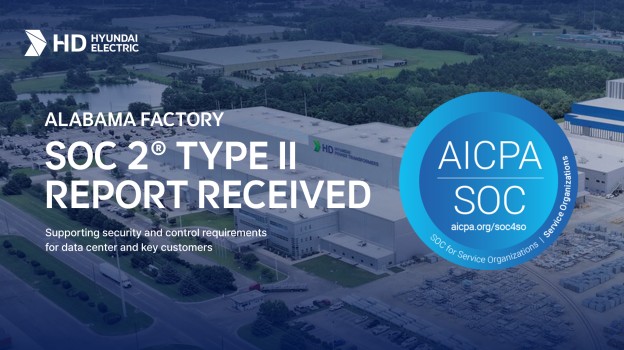
2026.06Alabama Factory Achieved SOC 2 Type II Report
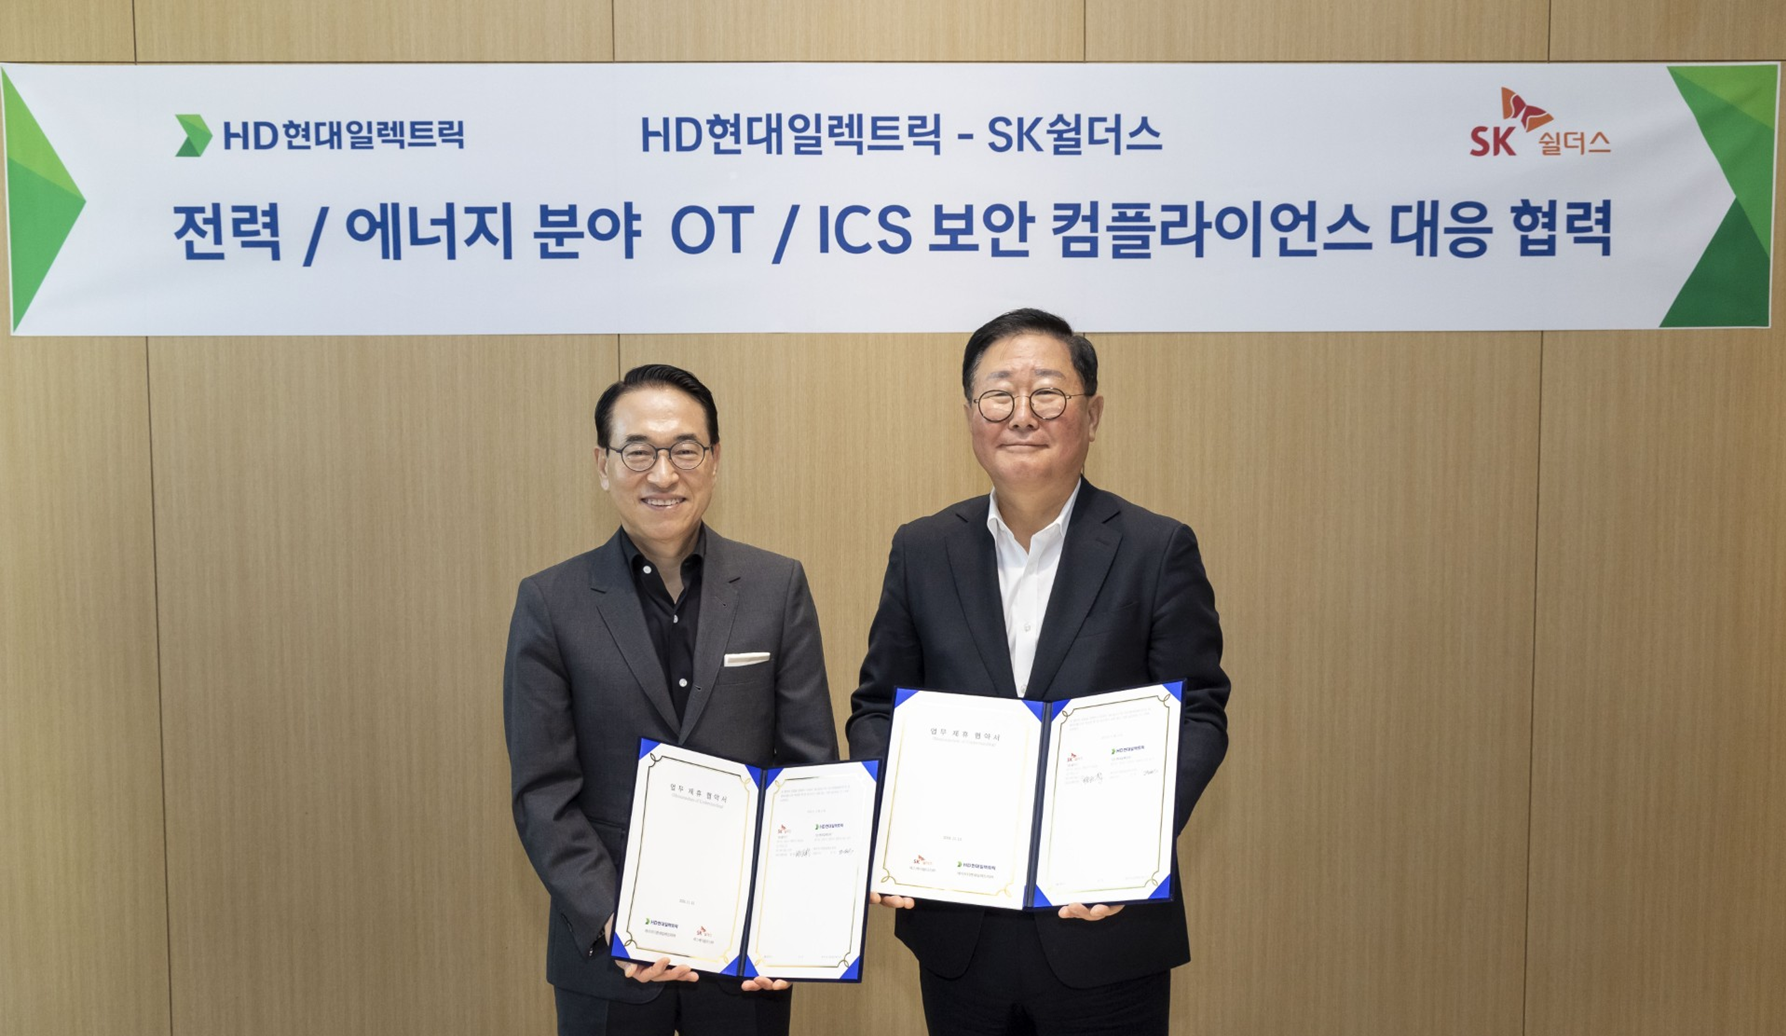
2024.11Strategic Partnership Established with SK Shieldus to Enhance OT/ICS Cybersecurity Capabilities
-

Security Check
Penetration Test
Code security review -

External audit
Regular audits by certification bodies
Response to security assessments requested by customers -

Internal audit
Conduct internal information security audits at least once a year
Review of vulnerability management, access control, and log management
-
2026
- 07HiPDS Motor Predictive Diagnostic System Certified to UR E27 (BV)
- 06HiPDS Motor Predictive Diagnostic System Certified to UR E27 (KR)
- 06IEC 62443-4-1 (ML2) Certification Achieved
- 06Alabama Factory Achieved SOC 2 Type II Report
- 05National Human Resources Development Consortium Agreement Signed (Korea Internet & Security Agency, KISA)
- 02Ulsan Transformer Factory Achieved SOC 2 Type II Report
-
2024
- 11Strategic Partnership Established with SK Shieldus to Enhance OT/ICS Cybersecurity Capabilities
- 01ISO/IEC 27001:2022 Certification Successfully Renewed
-
2021
- 01Obtained ISO/IEC 27001:2022 Certification (DNV)
Continuous Improvement Activities
-
Security Risk Management
- Analysis of new threats
- Risk assessment and remediation measures
-
Security Training
- Regular security training for employees
- Operation of security training for developers
-
Vulnerability Management
- Management of externally reported and internally discovered vulnerabilities
- Provision of security notices and patches