-
KOR
-
CONTACT
-
DOWNLOAD
- Main Product
- Power Transformer
- Gas Insulated Switchgear
- High-voltage Motor
- Generator
- MV/LV Switchgear
- Distribution Transformer
- Low-voltage Motor
- MV/LV Circuit Breaker
Search in other ways


Power Generation
Transmission
Distribution
Consumer/Factory


- 1~9, A~D
- 145kV GISHigh-voltage Switchgear
- 170kV GISHigh-voltage Switchgear
- 245/300kV GISHigh-voltage Switchgear
- 362kV GISHigh-voltage Switchgear
- 420/550kV GISHigh-voltage Switchgear
- 72.5kV GISHigh-voltage Switchgear
- 800kV GISHigh-voltage Switchgear
- Asset Management SolutionINTEGRICT
- BUSDUCT(BUSDUCT)Switchgear
- BUSDUCT(BUSWAY)Switchgear
- Cast Resin Distribution TransformerDistribution Transformer
- C-GISSwitchgear
- Crown Triton Motor Large FrameLow-voltage Motor
- DPRS, TPRS TransformerSpecial Transformers
- Drip-proof MotorLow-voltage Motor
- Dry-air switchgearGREENTRIC
- E~L
- Eco Shaft GeneratorGREENTRIC
- Emergency Switchboard Marine Switchgear
- Energy SolutionINTEGRICT
- Ex d/de/db/dbeb IIB/C MotorLow-voltage Motor
- Ex eb/ec IIC MotorLow-voltage Motor
- Furnace TransformerSpecial Transformers
- Gas Insulated TransformerSpecial Transformers
- General/Explotion Proof MotorHigh-voltage Motor
- Group Starter PanelMarine Switchgear
- High-Efficiency/Low Noise TransformerSpecial Transformers
- High Speed MotorElectric Motor
- HVDC Converter TransformerSpecial Transformers
- IE4 LV MOTORGREENTRIC
- IEEE841 MotorLow-voltage Motor
- L/M Voltage Circuit...L/M Voltage Circuit Breaker
- Low Voltage SwitchgearSwitchgear
- LV SwitchboardMarine Switchgear
- M~R
- Marine Distribution...Marine Distribution Transformer
- Marine Rotating MachineMarine Rotator
- Marine TransformerSpecial Transformers
- Medium/Low SpeedGenerator
- Mobile TransformerSpecial Transformers
- Motor Control Panel(MCP)Marine rotator
- MV SWGR for NuclearSwitchgear
- MV SwitchboardMarine Switchgear
- MV SwitchgearSwitchgear
- Natural Ester/Synthetic Oil-immersed Power TransformerSpecial Transformers
- Natural Ester/Synthetic Oil-immersed Power TransformerGREENTRIC
- Oil-immersed Distribution TransformerDistribution Transformer
- Phase Shift TransformerSpecial Transformers
- Power TransformerPower Transformer
- Quarry & Crusher Duty MotorLow-voltage Motor
- RMUSwitchgear
- S~Z
- SF6-Free GISGREENTRIC
- Shunt ReactorPower Transformer
- SVC TransformerSpecial Transformers
- Synchronous MotorHigh-voltage Motor
- TEAAC Type Squirrel-cage MotorHigh-voltage Motor
- TEFC MotorLow-voltage Motor(KS/IEC)
- TEFC MotorLow-voltage Motor(NEMA)
- TEFC Type Squirrel-cage MotorHigh-voltage Motor
- TEWAC Type squirrel-cage MotorHigh-voltage Motor
- Thruster StarterMarine Switchgear
- Totally-enclosed Wound-rotor MotorHigh-voltage Motor
- Trackside TransformerSpecial Transformers
- UL Explosion ProofLow-voltage Motor
- Weather Protected TEFC MotorHigh-voltage Motor
- Weather Protected Wound-rotor MotorHigh-voltage Motor
- Weather Protected WPIIHigh-voltage Motor
HD Hyundai Electric
Cybersecurity Center
HD Hyundai Electric has established a cybersecurity framework based on international security standards
to ensure the safe operation of its products and services. We have obtained global certifications including
ISO/IEC 27001, and manage security risks primarily through the CISO (Chief Information Security Officer)
organization.
- Cybersecurity Center
- Security Activity Notifier
- Security Notice
- Report Vulnerabilities
Introduction to Cybersecurity Services
-

Security Activity Notifier
International security certifications (such as ISO/IEC 27001) and product security-related
View Security Activity Notifier
assessment results are disclosed. -

Security Notice
You can check security notices such as vulnerabilities (CVEs) found in products,
View Security Notice
affected products, patch files, or mitigation
actions. -

Vulnerability Report
HD Hyundai Electric accepts product vulnerability reports in accordance with its Responsible Disclosure policy.
View Vulnerability Report
Notices
| Category | Title | Date of Registration |
|---|---|---|
| Certification | HD Hyundai Electric Obtains SOC 2 Type II Reports for Ulsan and Alabama Transformer Operations | 2026.09.17 |
| Certification | HD Hyundai Electric Achieves International Cybersecurity Standard IEC 62443-4-1 Certification | 2026.06.11 |
FAQ
|
Q. Where can I find security notices or information on vulnerability patches? We provide information on security vulnerability remediation status and security updates through the following sections.
※ The scope and timing of disclosure may vary depending on the severity of the vulnerability, product impact, and remediation status. |
|
Q. What qualifies as a reportable item? We accept reports regarding the following technical security vulnerabilities:
[In-Scope]
[Out-of-Scope]
If you are unsure whether an issue falls within the scope, please submit a report anyway, we will review it and provide guidance. |
|
Q. I’ve discovered a vulnerability; how do I report it? We highly value reports from individuals who discover security vulnerabilities and accept vulnerability reports through the following channels.
1. Website Submission: Please complete the reporting form on the Vulnerability Reporting Page. 2. Email Submission: Please send your report to hde.cybersecurity@hd.com
|
Introduction to Security Activity Notifier
HD Hyundai Electric systematically manages cybersecurity across all products and services based on international standards and global security frameworks.
-

Based on international standards
-

Conducting regular audits
-

Continuous Improvement
-

Transparent disclosure
Cybersecurity Management System
HD Hyundai Electric has established an Information Security Management System (ISMS) based on ISO/IEC 27001 and operates enterprise-wide cybersecurity governance,
including product security and service security.
-
Governance
- Operate a security organization led by the CISO
- Manage enterprise security policies and guidelines
-
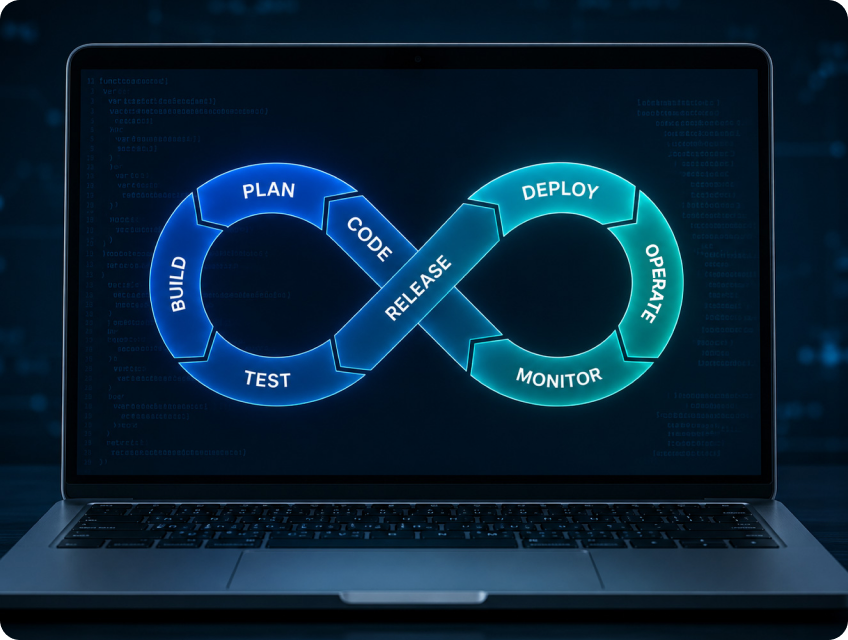
Secure SDLC
- Incorporate security requirements from the design stage
- Conduct static/dynamic analysis and security testing
-
Operations security
- Security Monitoring
- Manage vulnerabilities and operate the patch process
Certification and Standard Compliance Status
| Sortation | Certification/Standardization | Scope of application | Initial certification | Recent update | Link |
|---|---|---|---|---|---|
| Regulatory & Standards | IEC62443-4-1 | Enterprise Secure SDLC | 2026 | 2026 | View |
| Enterprise Security | SOC2 TYPE Ⅱ | Ulsan Transformer Factory, Alabama Factory | 2026 | 2026 | View |
| Product Security | UR E27 | Motor Predictive Diagnostic System(HiPDS) | 2026 | 2026 | |
| Enterprise Security | ISO/IEC 27001:2022 | Enterprise | 2021 | 2024 |
Audit and Evaluation Activities
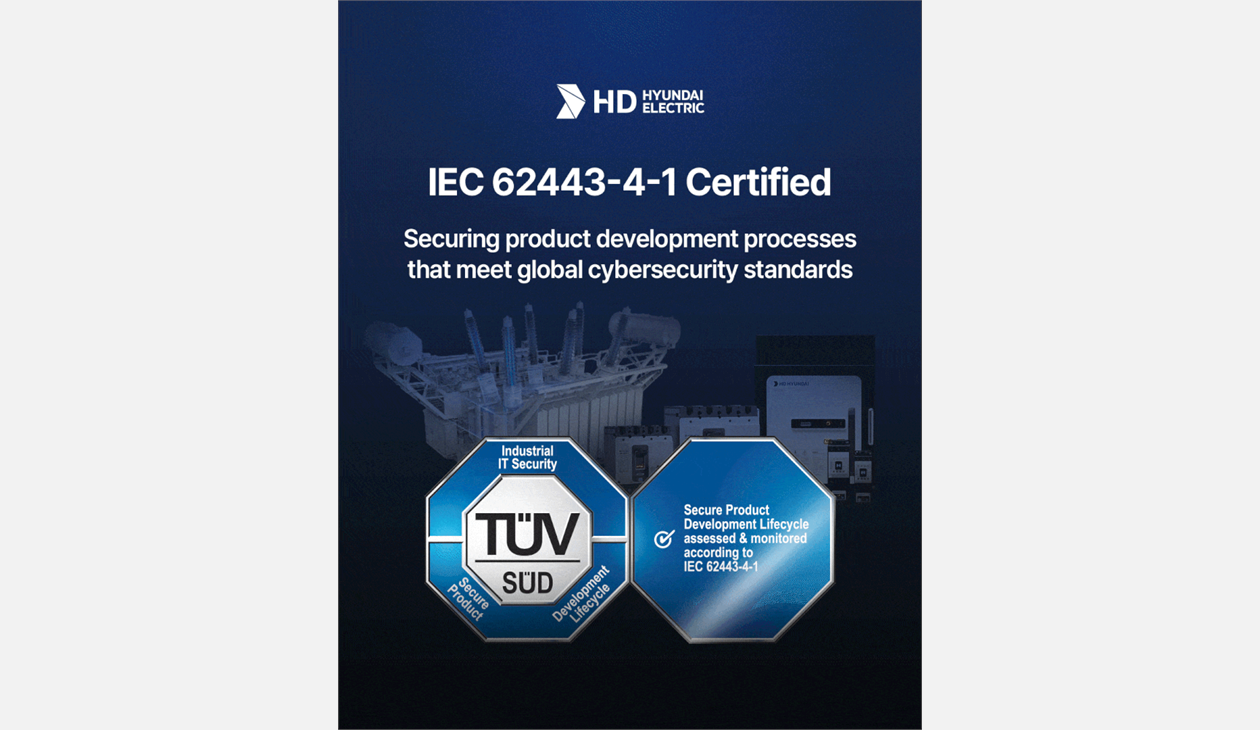
2026.06IEC 62443-4-1 (ML2) Certification Achieved
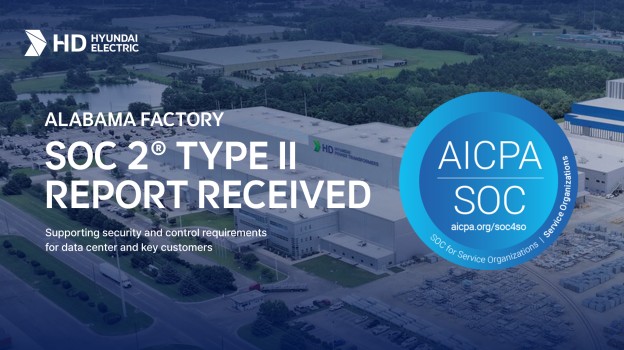
2026.06Alabama Factory Achieved SOC 2 Type II Report
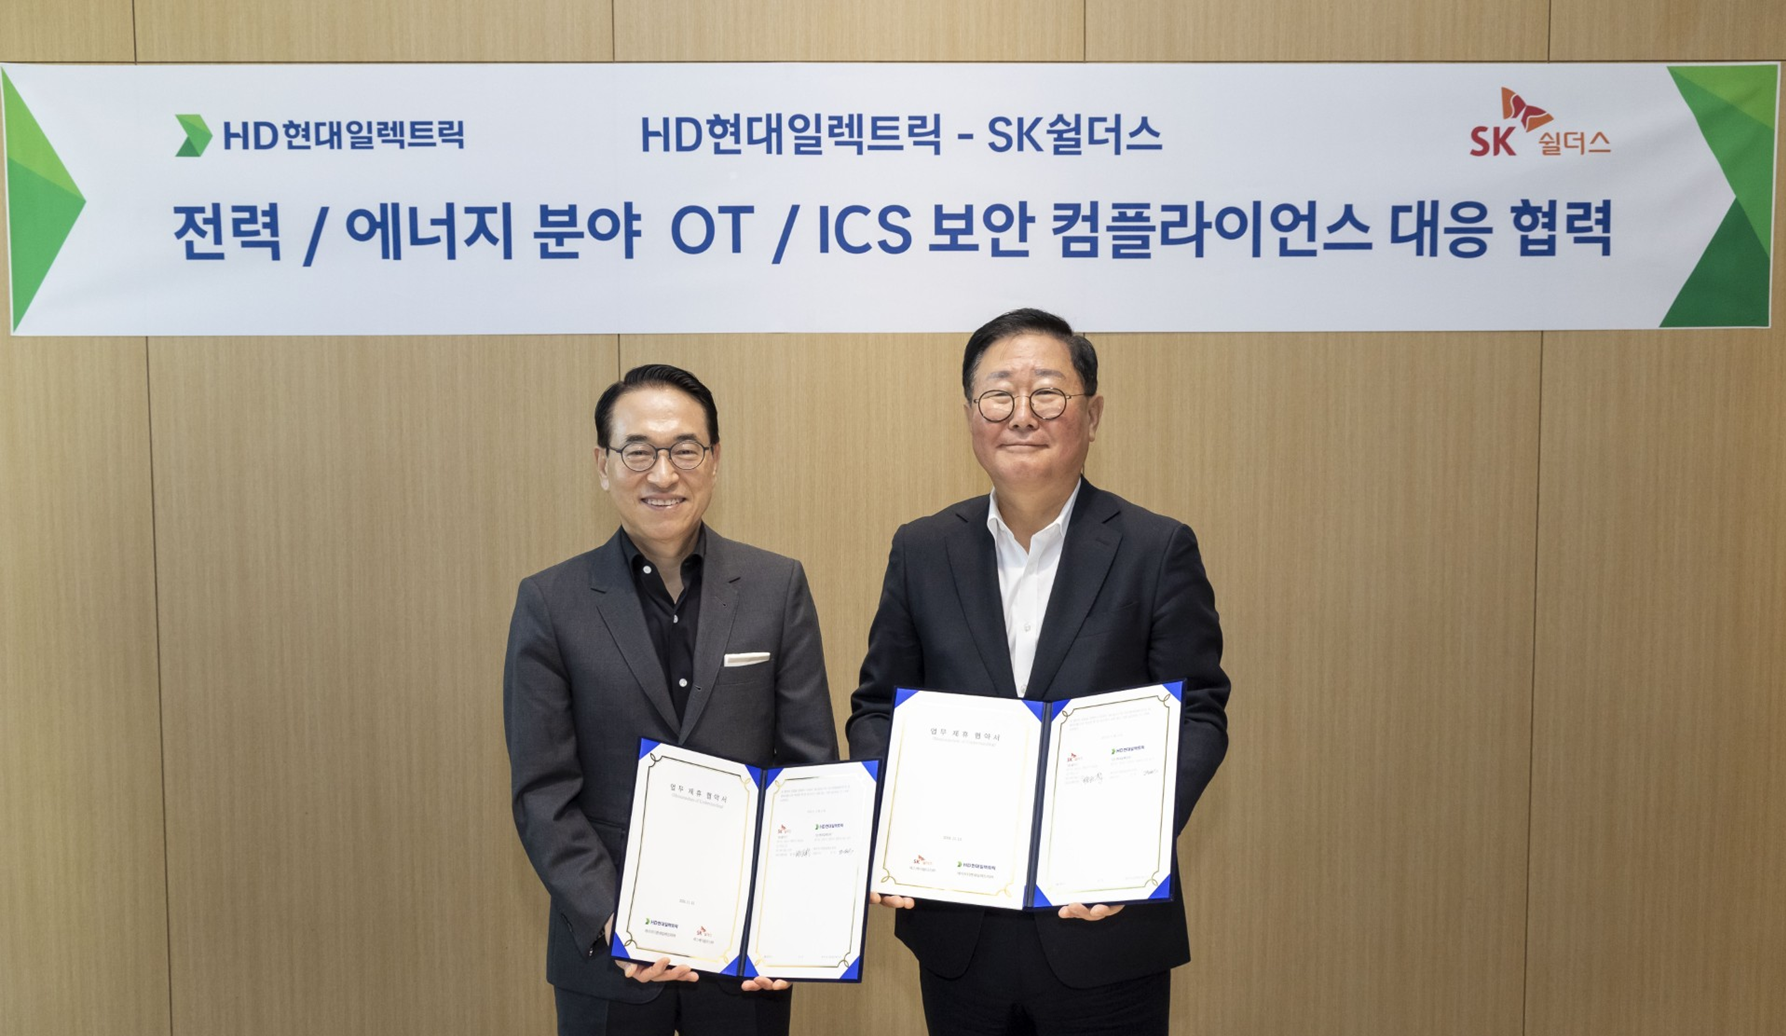
2024.11Strategic Partnership Established with SK Shieldus to Enhance OT/ICS Cybersecurity Capabilities
-

Security Check
Penetration Test
Code security review -

External audit
Regular audits by certification bodies
Response to security assessments requested by customers -

Internal audit
Conduct internal information security audits at least once a year
Review of vulnerability management, access control, and log management
-
2026
- 07HiPDS Motor Predictive Diagnostic System Certified to UR E27 (BV)
- 06HiPDS Motor Predictive Diagnostic System Certified to UR E27 (KR)
- 06IEC 62443-4-1 (ML2) Certification Achieved
- 06Alabama Factory Achieved SOC 2 Type II Report
- 05National Human Resources Development Consortium Agreement Signed (Korea Internet & Security Agency, KISA)
- 02Ulsan Transformer Factory Achieved SOC 2 Type II Report
-
2024
- 11Strategic Partnership Established with SK Shieldus to Enhance OT/ICS Cybersecurity Capabilities
- 01ISO/IEC 27001:2022 Certification Successfully Renewed
-
2021
- 01Obtained ISO/IEC 27001:2022 Certification (DNV)
Continuous Improvement Activities
-
Security Risk Management
- Analysis of new threats
- Risk assessment and remediation measures
-
Security Training
- Regular security training for employees
- Operation of security training for developers
-
Vulnerability Management
- Management of externally reported and internally discovered vulnerabilities
- Provision of security notices and patches
Security Vulnerabilities and Remediation Guide
HD Hyundai Electric provides information on security vulnerabilities (CVEs) identified in products and services and the actions taken accordingly.
| Announcement Date | Security Advisory | Affected Products | CVE ID | CVSS | Vulnerability Overview | Status | Download |
|---|---|---|---|---|---|---|---|
| No notices have been registered. | |||||||
Update and Patch Management
We provide the latest versions, updates, and patches for operating software.
| Change Type | SW Product Name | SW Version | Title | Product Family | Product Detail Classification | Release Date | Download |
|---|---|---|---|---|---|---|---|
| No patches have been registered. | |||||||
Vulnerability Information Guide
HD Hyundai Electric transparently discloses vulnerability information and provides guidance to enable customers to respond promptly.
-

1. Vulnerability Management Principles
HD Hyundai Electric identifies and evaluates security vulnerabilities according to international standards and responds by prioritizing them based on severity.
-

2. CVE Management Standards
Identified vulnerabilities are managed according to CVE standards when necessary.
-

3. Disclosure Principles
Vulnerability information is disclosed at an appropriate time, considering customer impact and whether security updates can be provided.
-

4. Customer Recommendations
We recommend applying the latest security updates for safe operations.
-

5. Vulnerability Reporting
Security vulnerabilities can be reported through the Vulnerability Report page.
Vulnerability Reporting Procedure
Reported vulnerabilities are systematically reviewed and processed according to the procedures below.
-

Report Submission
- After reviewing the submitted content, notification of receipt is sent via email
- Additional materials for the reproduction environment may be requested if necessary
-

Breach Analysis
- Cause analysis and testing following vulnerability verification
- Additional inquiries may arise during the testing process
-

Action Taken
- Cause analysis → Vulnerability patch development → Application
- CVE Code application/registration (if applicable)
- Sharing action results via security announcement upon patch completion
-

Closing
- Response to the vulnerability report ends after action is completed
- The reporter is notified separately of the final processing result
How to Report Vulnerabilities
To help maintain a safe security ecosystem, please report any vulnerabilities you discover using one of the methods below.
-
Email Report
For reports requiring security, please download and fill out the form below,
encrypt it using PGP, and submit it.
Sender information can be verified via email only, without the need for separate registration.Report Email Address
-
Go to Web Report Form
Website Report
You can easily report vulnerabilities by filling out the form on the web page.
Please enter the required information and submit.

Vulnerability Disclosure Policy
HD Hyundai Electric manages security vulnerabilities safely and systematically through Responsible Disclosure.
-

Principles of Responsible Disclosure
We disclose vulnerability information only after patches or mitigation measures have been established to prevent exploitation.
-

Protection of Researchers in Good Faith
We do not pursue legal liability for reports of security vulnerabilities made in good faith.
-

Vulnerability Handling Procedures
Received vulnerabilities undergo internal review, after which a severity assessment and remediation plan are established.
-

Scope and Method of Disclosure
Vulnerability information is disclosed via Security Advisories as necessary, in accordance with Common Vulnerabilities and Exposures (CVE) standards.
-

Communication with Whistleblowers
The vulnerability handling process and results are communicated to the whistleblower to the extent possible.
Important Notes Before Reporting a Vulnerability
- Actions that cause Denial of Service (DoS) are not permitted.
- Access to customer data and unauthorized account creation are prohibited.
- Please do not disclose discovered vulnerabilities to third parties.
- Please reproduce vulnerabilities within the minimum necessary scope.